CVSS:4.0AV:N / AC:L / AT:NPR:L / UI:N / …
SEVERITY ≠ PRIORITY
 Illustration of a working environment
Enrolment opening soon
Risk analysis and management
Learn to assess risk so the analysis leads to a decision. Build scenarios, compare assessment methods and control costs, and consider data uncertainty. Progress from foundations to applications in information systems, organizations and selected specialist domains.
PLN 990planned price including tax
In your browser · No installation · Tutor and narration
Open your browser. Start learning.
Do not spend your first evening configuring an environment. The application, tools and task context are in one place. You do not need Docker, a VPN, a virtual machine or paid software.
A virtual tutor walks you through the example and highlights important parts of the application, code or tool. Connect the instruction to what is happening on screen.
Narration explains the mechanism, decision and result. Pause the guidance, return to an earlier step and work through it at your own pace.
Take over in the exercise: change data, run a test or make a decision. Compare the result and improve your solution using the explanation.
One environment, without switching between a video and a local installation. Tools fit the topic: from HTTP requests and code to a terminal, calculator or document. Practice in simulators and prepared cases, without attacking other people's systems.
What will you be able to do?
Understand what you assess, where the data comes from and what changes the recommendation. Methods answer an organization's question, not merely produce a score.
You have a threat list but struggle to derive action from it.
Write an information-system scenario and identify data needed to assess likelihood and consequences.
You multiply numbers without knowing what the scales mean.
Compare qualitative assessment with a quantitative model, justify assumptions and test which most influence the result.
The analysis ends with a heatmap, without an owner or plan.
Compare control costs and effects, assign an owner and update the decision with new data.
Prepare material for discussions about controls, budget and responsibility. The course is standalone, with an emphasis on information systems. Numerical exercises use USD.
Connect each skill to a concrete work product. Return to explanations while you practice.
A syllabus backed by materials
See what makes up the syllabus: lessons, explanations, examples and exercises. The figures below describe different types of materials.
The figures describe the English-language source materials. The waiting list is for the planned Polish edition. These counts do not mean its translation is complete. Demonstration steps, examples and tasks are different units, not hours of video or counts of unique vulnerabilities.
Entry point
Available in Polish and English — you can switch language at any time. Command names, code snippets and standard identifiers remain in their original form.
How you learn
From a risk scenario through assumptions and calculations to a decision. The tutor guides the lesson; the workshop lets you test what changes the result.
Goal, constraints and inputs. Know what you are testing and why.
Watch a demonstration with tutor commentary, step by step.
Work with data, a tool or a scenario. Compare the result with your expectation.
Justify your decision and understand its limitations. Return to anything that needs improvement.
Exercises use simulators and selected mechanisms that run in the browser. They do not require attacking other people's systems.
Planned syllabus
Each area develops a specific skill. Learn not only the topic but also the action and outcome that learning leads to.
Learn standards and methods through original examples. The course does not replace full paid standards or professional qualifications. Exercise amounts are in USD.
Each topic includes a skill and a concrete exercise outcome.
I want to join the listDefine the decision the analysis supports, the time horizon and the service concerned. Connect threat source, event, weakness and consequence. Distinguish attacker action, human error and supplier failure scenarios.
Workshop with prepared data
Progress from identification through analysis and evaluation to action selection, communication and monitoring. Define criteria, risk appetite, tolerance and decision ownership. Learn ISO 31000's role as a reference for the whole process.
Case analysis
Distinguish test or observation results from planning assumptions and unavailable information. Assess source, date and data scope. Prepare questions whose answers could change the recommendation.
Workshop with prepared data
Define likelihood and consequence levels for a specific decision. Compare ordinal ratings with calculations and see what a shared matrix color hides. Record category rationale and escalation conditions.
Workshop with prepared data
Distinguish the chance of an event, expected event count and loss per event. Align time periods and units and compare financial consequences. Numerical examples use USD.
Workshop with prepared data
Learn FAIR concepts and separate event frequency from loss magnitude. Build a model with explicit assumptions and compare expected results with possible extreme consequences. Explain which decisions an average alone cannot resolve.
Workshop with prepared data
Compare assumption distributions, Monte Carlo results and event dependencies. Test which data most affects the recommendation and when better information is worth collecting. Learn the role of probabilistic risk analysis in broader assessment.
Workshop with prepared data
Compare avoidance, reduction, sharing or transfer, and risk acceptance. Connect action cost to the part of the scenario it should change. Record control effectiveness conditions, responsibility and verification.
Workshop with prepared data
Analyze a new test that challenges an earlier data-recovery assumption. Recalculate dependent results, compare options and update the recommendation. Preserve the earlier version so readers understand why the decision changed.
Workshop with prepared data
Connect information, business processes and supporting systems to confidentiality, integrity and availability. Practice asset-based and event-based approaches in the context of ISO/IEC 27005 and ISMS. Turn a technical finding into a scenario and treatment plan.
Workshop with prepared data
Use ISO 31000 and COSO ERM examples to connect risk to goals, accountability and management decisions. Check shared dependencies linking apparently separate problems. Prepare information useful for action selection and resource allocation.
Workshop with prepared data
Learn the relationship between NIST SP 800-30 and NIST RMF. Connect scenarios, control-effectiveness evidence and improvement plans. Distinguish an analyst's recommendation from the authorized person's decision to accept continued system use.
Workshop with prepared data
Use EBIOS RM concepts to analyze ecosystems, dependencies and strategic and operational scenarios. Identify relevant parties, objectives and the path to consequences. Compare protective actions at different scenario stages.
Workshop with prepared data
Learn OCTAVE Allegro concepts and examine information value and processing locations. Connect people, processes and technology in a threat description. Choose an assessment for the organizational context, not just a device list.
Workshop with prepared data
Trace data flows and abuse scenarios through STRIDE and PASTA perspectives. Connect a control to a test of its effectiveness. When comparing privacy approaches, also consider consequences for people whose data is processed.
Workshop with prepared data
Choose a further case for the problem: product reliability, system control, industrial installations, vehicles, processes, AI or medical devices. Learn each domain's characteristic questions and documents. These are original teaching applications, not substitutes for full standards and sector qualifications.
Case analysis
Analyze failure modes, causes and effects at successive product levels. Compare ratings and action priorities and check what confirms improvement effectiveness. Distinguish organizing a table from justifying reliability.
Workshop with prepared data
Map control, feedback and safety constraints. Recognize unsafe control actions and the circumstances in which they occur. Turn the analysis into a verifiable constraint or requirement.
Workshop with prepared data
Use IEC 62443-3-2 zone and conduit concepts in an industrial case. In an automotive case, explore ISO/SAE 21434 TARA concepts and consequences at the analyzed item's level. Connect scenarios, controls and required evidence for both.
Workshop with prepared data
Compare the questions asked by HAZOP, Bow-Tie and LOPA in prepared cases. Trace deviation, event and consequence and the role of barriers before and after an event. Check when a shared dependency undermines assumed control independence.
Workshop with prepared data
Connect intended AI use to metrics, affected groups and possible consequences. Use NIST AI RMF and ISO/IEC 23894 concepts to plan assessment and oversight. Record monitoring and reassessment conditions after system changes.
Workshop with prepared data
In an original ISO 14971-inspired case, distinguish hazards, hazardous situations and harm. Connect controls to evidence and information from use. Prepare an argument structure without equating the exercise with device approval.
Workshop with prepared data
Compare organizational, cybersecurity, privacy, quantitative and sector approaches by purpose and required data. Recognize when a method supports management, scenario analysis or calculation. Choose a sensible starting point and scope for further work.
Case analysis
Assemble the goal, scenario, sources, criteria, calculations and treatment options into one document. Identify the recommendation, owner and review triggers. Compare the initial version with analysis after data changes, preparing material for the responsible decision-maker.
Workshop with prepared data
In practice
Each case has context, a concrete action and an outcome. The goal is not to memorize a command but to understand why the result changed.
Build a service-interruption scenario and compare event prevention with consequence reduction. Align units, include costs and test which assumptions the recommendation depends on.
Work productA comparison model and justified recommendation for the process owner.
Read a further data-recovery test result and identify the assumption needing change. Recalculate the analysis, check the chosen action and preserve the earlier version.
Work productAn updated decision document describing the change, owner and monitoring plan.
Certificate of completion
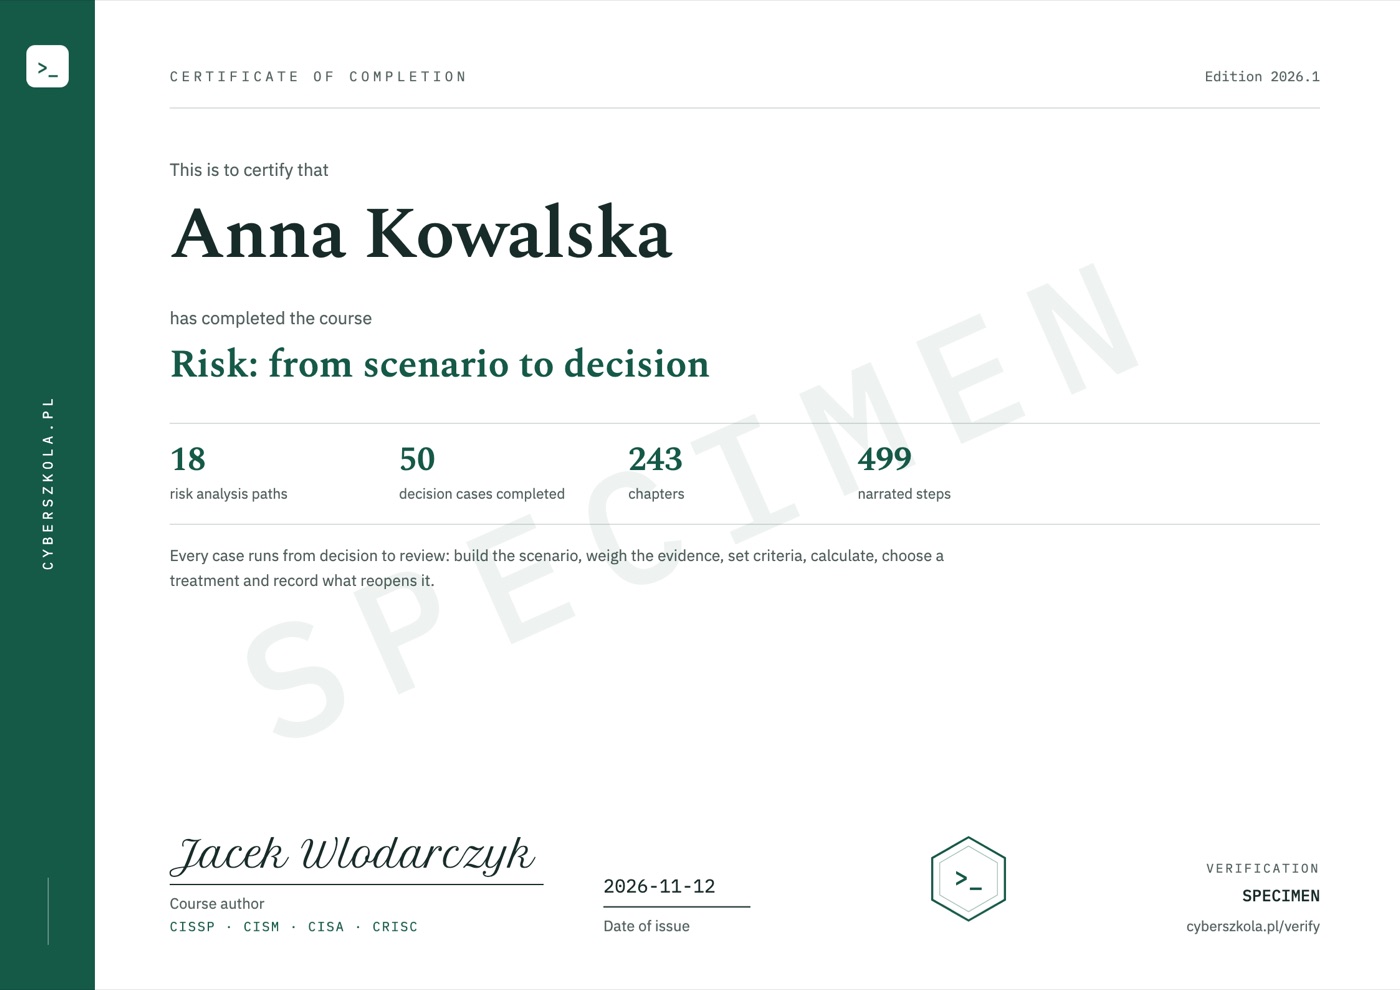
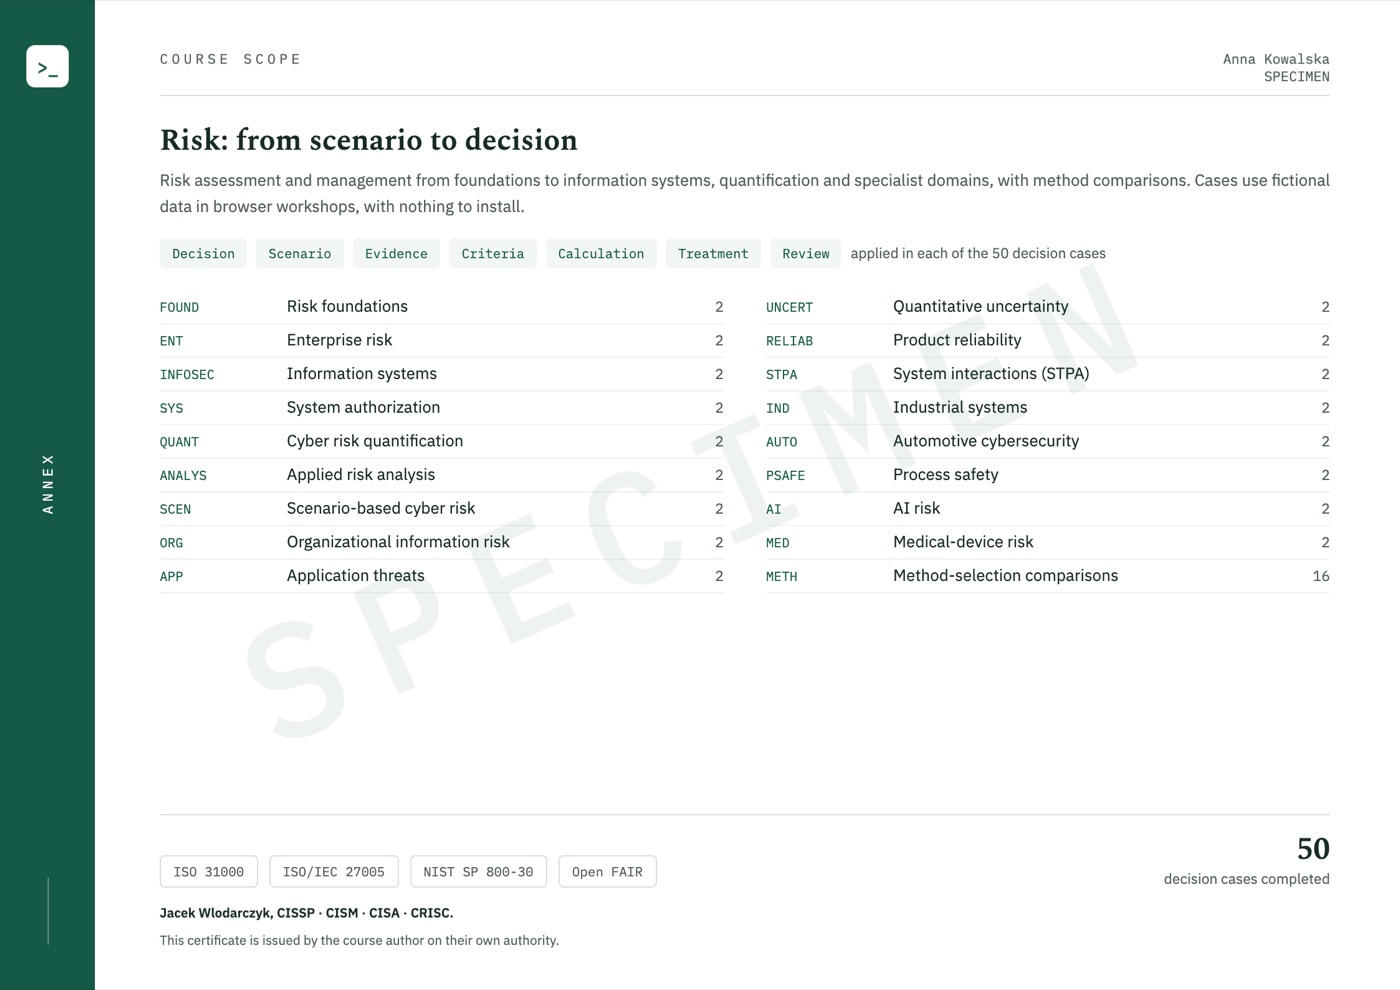
When you complete the course, the certificate is issued automatically and emailed to you. It shows your name, the date of issue and a unique code, and its second page lists the course scope.
Code verification: cyberszkola.pl/verify
Upcoming standalone course
Planned course price
Polish edition · Launch date not yet announced
Notify me at launchJoining is free. Before sales open, you will receive the date, full scope and purchase terms. We are not taking payments today. This is a separate interest list, not a place reservation or purchase.
For companies and teams
Compatible with LMS platforms including:
and other platforms that support e-learning standards.
Price for companies
Delivery into your company's own LMS from 50 licences.
Ask for a quoteWrite to kontakt@cyberszkola.pl: the number of people, the courses you want and your LMS, if you use one.
Project author
Creator of Cyberwiedza, cyberszkola and AI SecLabs. In these courses, I connect explanations of mechanisms with practice, observation and decisions you need to justify.
Running a command is not enough. What matters is what its output confirms, what it does not confirm and what the next step should be.
More about the authorBefore joining
No. This standalone course starts with the analysis purpose, scenario and meaning of data. CVSS appears as an example of technical assessment that must be distinguished from a complete risk decision.
No. Calculations start with units, probability, event counts and losses. More developed models support comparing assumptions and interpreting results. What matters is understanding data provenance and what changes the recommendation.
Choose a case close to your work to learn a domain's typical questions, dependencies and documents. Paths help select an analytical perspective. They do not replace full standards, industry practice or required qualifications.
No. This is an upcoming course announcement and an interest list. Joining is not a purchase, a place reservation or a commitment to pay.
The launch date, price and access terms will be announced before sales open. The interest list is how we send that information.
The course is available in Polish and in English — you can switch language at any time, and lessons, exercise explanations and narration exist in both. Commands, code and tool names keep their original syntax, as used in everyday work.
No. All course exercises run in your browser on a computer with internet access. Training applications, terminals, editors and workshops are part of the platform. You do not install Docker, a virtual machine or a VPN, and you do not need paid external tools.
No. You work in an interactive environment. A virtual tutor highlights important elements, and narration explains the action and its result. Pause the lesson, return to earlier steps and run your own experiments. This guidance is built into the course, not individual consultation with a person.
No. You use training applications, simulators and prepared data. Learn the mechanism and its limitations in a safe environment. External resources are supplementary, not required to complete the exercises.
Yes, a certificate of completion. When you complete the course, you receive a certificate in English with a unique code that anyone can check at cyberszkola.pl/verify. It confirms completion of the course and is issued by the author; it is not an industry certification. We do not promise employment.
No. These are independently authored courses using public references and original cases. They do not replace licensed standards, accreditation or qualifications required in regulated industries.
Join the waitlist
Leave your email address. We will send you news of enrollment, the syllabus and first-edition terms. You will not need to keep checking this page.
Planned price: PLN 990 including tax